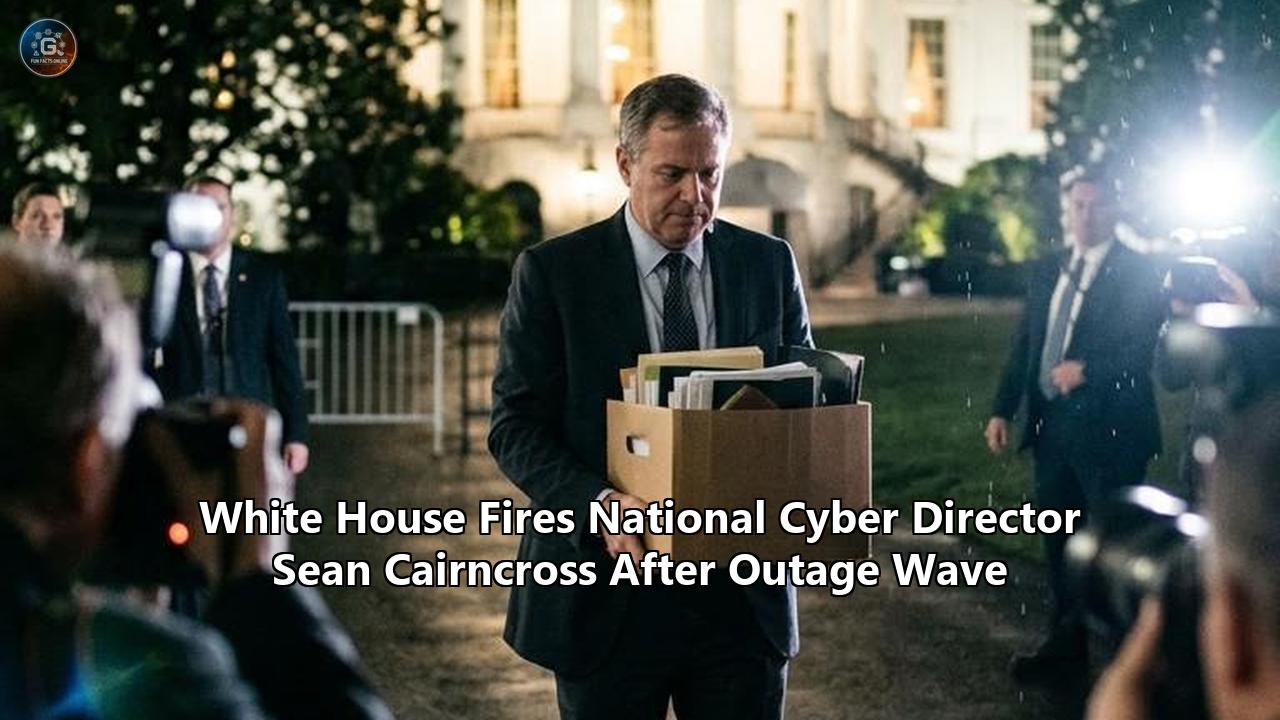
The White House abruptly removed National Cyber Director Sean Cairncross from his post on November 19, 2026, culminating a frantic week of nationwide infrastructure failures that crippled commercial aviation, snarled enterprise computing, locked consumers out of major financial institutions, and temporarily darkened classified communications inside the National Security Agency. President Donald Trump approved the immediate dismissal at the urging of his newly installed White House Chief of Staff, Stephen Miller, who argued behind closed doors that Cairncross lacked the technical credentials and operational command necessary to manage the nation’s cybersecurity apparatus during an active systemic crisis.
The decision that saw Sean Cairncross fired sent immediate shockwaves through the cybersecurity and defense communities. To fill the void, the administration tapped Kirsten Davies, the Senate-confirmed Chief Information Officer for the Department of Defense, to assume the directorship in an acting capacity. Secretary of State Marco Rubio publicly endorsed the appointment, signaling an urgent effort by the national security cabinet to project competence amid escalating domestic disruption.
The ouster cuts to the heart of an enduring structural problem in modern governance. While the public and political leadership instinctively view catastrophic digital failures through the lens of hostile nation-state attacks, technical investigators quickly determined that the mid-November collapse was largely an unforced error. Homeland Security Secretary Markwayne Mullin told lawmakers on Capitol Hill that federal investigators were "98% confident" the outages were not the product of foreign cyber warfare, but rather a catastrophic convergence of routine software updates, maintenance misconfigurations, and systemic cascading dependencies across enterprise platforms.
The Cairncross dismissal serves as a case study in the intersection of digital vulnerability and political accountability. It demonstrates what occurs when an advisory office designed for long-term strategic doctrine is thrust into the role of operational scapegoat, and how the appointment of political loyalists to hyper-technical posts leaves the executive branch intellectually exposed when critical national infrastructure breaks down.
Anatomy of the Collapse: A Forensic Look at the Mid-November Outages
To understand why the White House moved so aggressively against its cyber director, one must trace the timeline of technical failures that seized the country over the course of seven days. Unlike isolated cyber incidents, this disruption hit four foundational pillars of modern American life simultaneously: civil aviation, commercial banking, enterprise software, and classified defense communications.
MID-NOVEMBER 2026 OUTAGE TIMELINE
========================================================================================
[Day 1-2] Global Cloud Disruption: Microsoft 365 and identity federation pipelines fail.
          Hundreds of millions of enterprise users lose communications.
[Day 3]   Aviation Gridlock: FAA telecommunication routing synchronization collapses.
          National ground stop declared; ~20,000 commercial flights delayed/grounded.
[Day 4]   Financial Systems Freeze: Core digital banking gateways fail at Chase and regional
          lenders; automated clearing operations and consumer interfaces timeout.
[Day 5]   Intelligence Blackout: National Security Agency internal classified networks
          experience localized communication disruption.
[Day 6]   Capitol Hill Scrutiny: DHS Secretary Markwayne Mullin testifies disruptions stem
          from technical maintenance and updates, not state-sponsored cyber warfare.
[Day 7]   West Wing Execution: Chief of Staff Stephen Miller pushes ouster;
          Sean Cairncross fired; Kirsten Davies named Acting Director.
========================================================================================
The Enterprise Cloud Domino
The crisis began with a routine configuration deployment within Microsoft’s enterprise identity and productivity ecosystem. A synchronization error between legacy hybrid infrastructure and modern cloud directories triggered an authentication loop across Microsoft 365 services. Within hours, hundreds of millions of corporate, healthcare, and municipal employees found themselves locked out of email, collaboration channels, and document repositories.
Because modern enterprises rely heavily on single sign-on (SSO) frameworks and federated identity services, this initial disruption was not contained within office software. It acted as an upstream blocker for thousands of downstream third-party applications that require continuous, automated identity handshakes to function.
Aviation Routing and the FAA Ground Stop
Before enterprise IT teams could stabilize identity directories, the Federal Aviation Administration suffered a devastating breakdown in its core flight routing telecommunication switches. Air traffic control centers reported intermittent data loss in flight plan processing and automated radar handoffs, forcing regulators to initiate an unprecedented national ground stop.
The result was logistical chaos. Nearly 20,000 flights were delayed, diverted, or canceled nationwide, stranding hundreds of thousands of travelers across major hubs. While the FAA insisted that physical flight safety had not been compromised due to manual reversion procedures, the near-total shutdown of commercial airspace illuminated the extreme fragility of legacy transportation routing systems running on aging, patched telecommunications backbones.
Financial Service Gateway Timeouts
Twenty-four hours later, the shockwaves struck retail banking and payment clearing systems. Customers of JPMorgan Chase and several large regional financial institutions encountered widespread access outages across digital banking apps and automated clearinghouse operations.
Financial engineering teams discovered that internal microservice routing layers, straining under delayed batches caused by the earlier cloud disruptions, had tripped automated rate-limiting safety valves. While consumer funds remained secure, transactions stalled, corporate payroll runs were delayed, and credit card processing experienced localized blackouts at merchant points of sale.
The Intelligence Community Blackout
The breaking point for the White House came when the crisis crossed the threshold from civilian inconvenience to national security vulnerability. An internal communications network utilized by the National Security Agency at its Fort Meade headquarters experienced an unannounced outage, knocking secure terminals offline and disrupting intra-agency coordination.
For an intelligence community charged with maintaining unbroken situational awareness across global combat commands and monitoring adversary communications, an internal blackout represents an acute vulnerability. Although technical forensic teams quickly determined the NSA disruption was caused by an internal security patch deployment gone awry rather than an offensive strike by a foreign adversary, the optics were disastrous.
When Secretary Mullin arrived on Capitol Hill, he attempted to calm financial markets and the public by testifying that he was "98% confident" no adversary was pulling the strings. Yet Mullin acknowledged under oath that he had "absolutely not" seen so many catastrophic infrastructure breakdowns concentrated in such a compressed timeframe. For an administration that staked its identity on projecting strength, technological dominance, and national security vigor, the cascade of failures proved politically untenable.
Case Subject Profile: Political Patronage Meets Technical Governance
The rise and fall of Sean Cairncross highlights a structural debate that has plagued the Office of the National Cyber Director (ONCD) since its statutory inception: should the cyber director be a deeply technical domain engineer, or a politically connected administrative fixer?
Cairncross was decidedly the latter. A veteran attorney, he spent the bulk of his career within the machinery of the Republican Party. He served as chief counsel and deputy executive director for the National Republican Senatorial Committee, later rising to chief operating officer of the Republican National Committee during the 2016 and 2024 presidential campaigns.
SEAN CAIRNCROSS: CAREER TRAJECTORY TO ONCD
----------------------------------------------------------------------------------------
• 2007–2009: Chief Counsel, Republican National Committee
• 2009–2013: Deputy Executive Director & General Counsel, NRSC
• 2015–2016: Chief Operating Officer, Republican National Committee
• 2017–2018: Deputy Assistant to the President & Senior Advisor to Chief of Staff
• 2019–2021: Chief Executive Officer, Millennium Challenge Corporation (MCC)
• 2024:      Chief Operating Officer, Republican National Committee
• Aug 2025:  Confirmed by U.S. Senate as National Cyber Director
• Nov 2026:  Terminated following multi-sector national outage wave
----------------------------------------------------------------------------------------
During the first Trump administration, Cairncross held roles as a senior adviser to the White House Chief of Staff before winning Senate confirmation to lead the Millennium Challenge Corporation (MCC), a bilateral foreign aid agency tasked with administering development grants. He had no background in low-level software engineering, defensive telemetry, industrial control systems, or critical infrastructure operations.
When President Trump nominated him in February 2025 to serve as National Cyber Director, the selection was seen as an explicit effort to install an ideological loyalist who would rein in federal cybersecurity regulations, slash compliance mandates for private industry, and align the office’s priorities with the White House’s broader economic platform. Cairncross cleared the Senate in August 2025.
In March 2026, his office unveiled a seven-page National Cyber Strategy. The document broke sharply with the defensive, resilience-focused posture of previous administrations. Instead, it articulated an aggressive philosophy:
- Prioritizing offensive cyber deterrence by "introducing costs and consequences" on foreign adversaries before they could execute breaches.
- Rolling back civilian cybersecurity reporting mandates and compliance structures to spur private enterprise velocity.
- Positioning the federal government to establish undisputed global superiority in artificial intelligence, which Cairncross frequently championed as "Super Intelligence".
- Modernizing federal IT architecture by stripping away procurement hurdles.
For several months, Cairncross won praise from administration allies for leading high-level strategy discussions with major artificial intelligence and venture capital leaders. He framed his mission around strategic geopolitical positioning rather than the tedious, complex mechanics of code auditing, patch management, and network redundancy.
When technical reality asserted itself in November 2026, that strategic posturing collapsed. When corporate boardrooms, airline dispatch centers, and the National Security Agency went dark, the White House did not need a speechwriter on AI dominance. It needed an executive capable of interrogating cloud architects, dissecting configuration pipelines, and demanding operational answers from defense and intelligence chiefs. Cairncross could not perform that function.
The West Wing Power Shift: The Mechanism of the Ouster
The speed with which Cairncross was terminated cannot be divorced from the evolving internal power structure of the White House. Earlier in November 2026, Susie Wiles stepped aside as White House Chief of Staff, replaced by Stephen Miller. Miller’s ascension marked a dramatic shift toward tighter operational discipline, heightened ideological enforcement, and zero tolerance for perceived public incompetence.
Inside the executive branch, the internal campaign that left Sean Cairncross fired had been brewing long before the outage wave escalated. Miller had harbored deep skepticism regarding Cairncross’s qualifications from the moment he entered the West Wing, privately warning advisers that placing an election lawyer in charge of the country’s cyber policy was an invitation to disaster.
WEST WING DYNAMICS & PERSONNEL RECONFIGURATION
----------------------------------------------------------------------------------------
Stephen Miller                   Donald Trump                    Sean Cairncross
(White House Chief of Staff)     (President of the United States)(Former Cyber Director)
        │                                │                                │
        ├─ Initiates personnel review    ├─ Approves firing├─ Released from duties
        ├─ Cites lack of technical       └─ Endorses pivot to            └─ Issues departure
        │  credentials       operational posture     statement defending
        └─ Moves immediately to tap                                         "Super Intelligence"
           Pentagon CIO Kirsten Davies                              legacy
----------------------------------------------------------------------------------------
When the cascade of outages disrupted travel for thousands of voters, stalled commercial banking, and breached Fort Meade’s operational tempo, Miller moved decisively. Administration officials revealed that Miller presented Trump with a clear assessment: the White House was being mocked for championing "Super Intelligence" while it could not keep its own airplanes flying or its premier spy agency’s communications online. Miller made the case that Cairncross lacked the respect of career intelligence officials and could not authoritatively represent the administration before television cameras or congressional oversight committees.
President Trump approved the firing, with senior officials later confirming that the president fully backed removing Cairncross because he lacked the specific cyber credentials to perform the role under pressure.
In a farewell statement issued following his removal, Cairncross sought to protect his standing, praising the president and defending his policy agenda:
"It has been the honor of a lifetime to serve President Donald J. Trump. I leave my role as Director of Cyber incredibly proud of our work to strengthen America's cybersecurity, protect our critical infrastructure, confront foreign threats, and position America to lead the world in Super Intelligence. None of it would have been possible without President Trump's extraordinary leadership. He is a prolific leader who thinks bigger, moves faster, and inspires those around him to deliver."
Behind the diplomatic language, the execution was total. Miller did not wait for a protracted transition period. He immediately placed Kirsten Davies in the role, relying on her status as a Senate-confirmed Department of Defense official to bypass immediate confirmation obstacles while installing a proven technocrat at the helm.
Dissecting the Institutional Vacuum: The Structural Flaw of ONCD
Analyzing why Sean Cairncross fired became the administration’s immediate political remedy requires dissecting the disconnect between the statutory design of the Office of the National Cyber Director and the public’s expectations during a national digital crisis.
THE U.S. CYBERSECURITY GOVERNANCE TRIANGLE
========================================================================================
                      [OFFICE OF THE NATIONAL CYBER DIRECTOR]
                                     (ONCD)
                     * White House Policy, Strategy & Budget *
                       Advisory Authority, No Direct Levers
                                    /      \
                                   /        \
                                  /          \
   [CYBERSECURITY & INFRASTRUCTURE]          [U.S. CYBER COMMAND & NSA]
         SECURITY AGENCY (CISA)                      (USCYBERCOM)
    * Civilian Operational Defense *          * Military Offensive/Defensive *
    Vulnerable infrastructure, Incident       Signals Intelligence, Foreign Intel,
    Response, Private Sector Liaison  Forward Operations
========================================================================================
Established by Congress in the National Defense Authorization Act for Fiscal Year 2021 following recommendations from the Cyberspace Solarium Commission, ONCD was designed as an executive coordinating body. Its original architects envisioned a cyber equivalent of the National Security Advisor: a principal adviser who sits feet from the Oval Office, aligns federal cyber budgets across cabinet agencies, crafts defensive strategies, and mediates interagency jurisdictional disputes.
Crucially, ONCD was never granted operational command authority.
- The National Cyber Director does not control defensive incident response teams. That authority belongs to the Cybersecurity and Infrastructure Security Agency (CISA), housed within the Department of Homeland Security.
- The National Cyber Director does not command cyber warfare forces, offensive intrusions, or signals intelligence. That authority rests with the dual-hatted commander of U.S. Cyber Command and the National Security Agency.
- The National Cyber Director does not manage the software procurement or infrastructure engineering of independent federal agencies, which operate under their own Chief Information Officers and Inspectors General.
This institutional arrangement creates an accountability mismatch. When systems crash, the media, the public, and the President do not distinguish between strategic policy coordination and operational incident triage. They view the National Cyber Director as the nation's "Cyber Czar". When private companies like Microsoft or telecommunications backbones experience systemic failures, the National Cyber Director has zero statutory power to compel code rollbacks, seize infrastructure, or force architecture changes.
Cairncross was effectively held accountable for events occurring entirely within operational domains over which he possessed neither statutory authority nor technical visibility.
Compounding this dynamic was a critical leadership vacuum across the rest of the federal cyber apparatus. At CISA, the administration’s nominee for director, Michael LoSapio, saw his nomination stall in the Republican-controlled Senate after contentious confirmation hearings regarding his public statements surrounding the January 6, 2021 Capitol attack. With CISA operating without permanent leadership and Cairncross focusing almost entirely on high-level AI policy, the federal government entered mid-November with nobody actively steering operational risk across the civilian tech stack.
Five Systemic Principles Extracted from the Crisis
Beyond the political drama of the West Wing, the ouster of Cairncross provides a valuable blueprint for diagnosing the modern state of technological risk. Examining the incident yields five critical principles that illuminate broader vulnerabilities in federal and corporate systems.
1. Configuration Fragility and Monoculture Outweigh Foreign Cyber Warfare
For decades, national security planners have conditioned the public to fear a "Digital Pearl Harbor"—a coordinated, weaponized strike by elite state actors in Beijing, Moscow, or Tehran designed to take down electric grids, banking systems, and air traffic control.
The November 2026 outages demonstrated that modern digital infrastructure does not require a hostile nation-state adversary to collapse. The catastrophic outcomes that planners spent decades attributing to foreign military units were accomplished through routine operational missteps: an enterprise directory configuration error, an unverified telecommunications routing update, and an internal software patch deployed into a classified environment without sufficient canary testing.
The underlying villain is architectural monoculture. When the global economy, the federal civil service, and military branches consolidate their enterprise identities, cloud processing, and data hosting into a handful of hyper-scale providers, they create single points of failure with massive blast radiuses. When a core provider stumbles, the impact cascades unpredictably through dependent sectors, transforming an isolated engineering bug into a multi-sector crisis.
2. Strategy Without Operational Levers Breeds Performative Governance
The ONCD's structural flaw is that it separates strategic accountability from operational authority. If a White House official is charged with ensuring the resilience of critical infrastructure, that official must possess either direct regulatory oversight over key commercial tech providers or operational leverage over civilian agency deployments.
Cairncross’s tenure demonstrated what happens when this leverage is absent. The office drifted toward performative policy: drafting seven-page strategy memos, delivering speeches at industry summits, and hosting roundtables with Silicon Valley executives on the distant promise of artificial intelligence. Performative strategy creates an illusion of security during tranquil periods, but evaporates instantly the moment complex distributed software systems experience systemic failures.
3. Offensive Posturing Cannot Compensate for Defensive Vulnerability
The Trump administration’s March 2026 cyber strategy explicitly prioritized offensive cyber deterrence—promising to impose severe, asymmetrical costs on adversaries before they could execute attacks against American networks.
THE DETERRENCE VS. RESILIENCE PARADOX
┌────────────────────────────────────────────────────────────────────────┐
│ OFFENSIVE DETERRENCE (The Cairncross Strategy)                          │
│ • Focus: Threat hunting, striking adversary command-and-control,      │
│   imposing economic and kinetic consequences.           │
│ • Blind Spot: Useless against internal maintenance bugs,               │
│   software supply-chain decay, and vendor configuration drift.│
├────────────────────────────────────────────────────────────────────────┤
│ SYSTEMIC RESILIENCE (The Structural Requirement)                       │
│ • Focus: Fault-tolerant architectures, decoupled microservices,        │
│   isolated directory backups, rigorous staged rollout validation.      │
│ • Reality: The only defense against catastrophic self-inflicted        │
│   downtime across critical civil and military networks.               │
└────────────────────────────────────────────────────────────────────────┘
The events of mid-November revealed the core limitation of this offensive doctrine. You cannot deter a misconfigured domain controller. You cannot launch an offensive cyber strike against a broken software deployment pipeline.
By framing cybersecurity primarily as an arena of offensive geopolitical competition, the administration neglected the unglamorous, foundational work of defensive resilience: continuous validation, architectural decoupling, mandatory multi-cloud failover mechanisms, and rigorous regression testing for federal updates. When the critical infrastructure broke, the nation’s offensive capabilities were rendered entirely irrelevant.
4. Technocratic Domain Fluency Is Non-Negotiable in Mission-Critical Posts
The appointment of political loyalists to executive agencies is an established feature of the American presidency. However, cybersecurity and infrastructure protection represent domains where technical domain literacy is directly tied to national continuity of operations.
When an enterprise crisis unfolds, the executive in charge must possess the technical literacy to:
- Parse low-level incident telemetry and forensic logs without relying on sanitized corporate briefings.
- Ask probing, adversarial questions of vendor Chief Technology Officers to verify root-cause analyses.
- Distinguish between an active adversary conducting lateral movement and an operational routing failure.
- Coordinate immediate containment measures that balance security constraints against commercial and societal necessity.
Stephen Miller’s realization that Cairncross "lacked the credentials" to manage the job under pressure underscores an unavoidable truth. In technical crises, generalist political acumen cannot substitute for deep domain expertise. When an official cannot grasp the underlying architecture of a failing network, they cannot lead its recovery.
5. AI Evangelism Distracts from Foundational Infrastructure Debt
Throughout 2025 and 2026, Cairncross placed the Office of the National Cyber Director at the forefront of the administration's push to deregulate and accelerate generative artificial intelligence and autonomous systems. He frequently spoke of advancing "Super Intelligence" as the ultimate guarantor of American national security.
The November crisis served as a sobering correction. The systems that failed were not autonomous frontier models; they were legacy airline dispatch databases, core telecommunications routing switches, enterprise identity gateways, and classified intranet nodes.
Chasing speculative, forward-looking technologies while allowing foundational digital infrastructure to rot from technical debt creates an untenable dichotomy. An empire racing toward advanced artificial intelligence while running its air traffic control and commercial financial networks on fragile, monolithic software backbones builds its technological future on sand.
Enter Kirsten Davies: The Pentagon Technocrat Takes the Reins
The White House’s rapid appointment of Kirsten Davies to replace Cairncross marks a significant tactical pivot from political management to technocratic crisis management.
LEADERSHIP PROFILES: THE CONTRAST
========================================================================================
METRIC                   SEAN CAIRNCROSS                KIRSTEN DAVIES
----------------------------------------------------------------------------------------
Primary Background       Election Law, Party Politics   Enterprise Cyber, Defense Tech
Prior Role               RNC Chief Operating Officer    DoD Chief Information Officer
Domain Expertise         Legal Strategy, Governance     Network Architecture, Threat Ops
Senate Confirmation      Aug 2025 (Confirmed as NCD)    Confirmed as DoD CIO
Primary Stated Focus     Offensive Deterrence, AI Systemic Resilience, Interoperability
========================================================================================
Davies brings a radically different profile to the West Wing. As Chief Information Officer for the Department of Defense, she served as the principal adviser to Secretary of Defense Pete Hegseth on information technology modernization, information assurance, enterprise cloud architecture, and defense-wide cybersecurity defense. Prior to her government service, Davies accumulated decades of private-sector experience as a Chief Information Security Officer (CISO) and technology executive across multinational financial, manufacturing, and telecommunications enterprises.
Her elevation signals several clear operational shifts:
Operational Credibility
Unlike Cairncross, Davies speaks the language of low-level engineering, network packet inspection, and zero-trust implementation. She has spent her career auditing vendor pipelines, managing sovereign defense networks, and negotiating enterprise Service Level Agreements. When she convenes meetings with the chief executives and software architects of Microsoft, cloud infrastructure providers, and airline conglomerates, she operates as an informed technical counterpart rather than a political liaison.
Restoring Military and Intelligence Confidence
Davies’ dual position bridges the bitter divide that emerged between the civilian cyber office and the defense-intelligence apparatus at Fort Meade. By leveraging her existing relationships within the Pentagon, the Joint Staff, and the intelligence community, she brings immediate operational cohesion to an administration reeling from internal blackouts. Her immediate public endorsement by Secretary of State Marco Rubio illustrates the national security cabinet’s desire to rally around a steady, qualified operator.
The Limitations of the "Acting" Capacity
Davies enters the role in an acting capacity, which introduces severe statutory and operational complications. Because the National Cyber Director is a Senate-confirmed position, an acting official faces strict legal limits under the Federal Vacancies Reform Act regarding how long they can exercise statutory authorities without formal nomination.
Simultaneously managing the Department of Defense’s massive, complex information architecture while running White House cyber policy creates an unsustainable operational burden. Unless the administration officially nominates her and secures Senate confirmation, her tenure remains a temporary patch rather than a permanent institutional solution.
Washington's Squeezed Clock: Senate Transition and Nomination Gridlock
With Sean Cairncross fired and Davies operating merely in an acting capacity, the Trump administration faces a rapidly closing legislative window. The Republican Party held control of the United States Senate through late 2026, but the November 2026 midterms swept Democrats back into the Senate majority beginning in January 2027.
THE NOMINATION BATTLESPACE: CLOCK RUNNING OUT
========================================================================================
NOVEMBER 2026                DECEMBER 2026                  JANUARY 2027
[Cairncross Fired] ───────►  [Narrow Lame-Duck Window] ───► [New Senate Convenes]
Davies steps in as acting;   GOP-controlled Senate must     Democrats assume Senate majority;
CISA post remains empty;     rush confirmation or risk      aggressive oversight hearings;
Outage investigation opens.  divided-government blockade.   hostile confirmation terrain.
========================================================================================
This dynamic places the White House in a precarious dilemma:
- If the administration wants to install a permanent National Cyber Director without facing aggressive bipartisan obstruction, it has only a few weeks during the post-election lame-duck session to submit a nominee and force a floor vote.
- Pushing a permanent nominee through the Senate Judiciary and Homeland Security committees within this compressed timeframe is nearly impossible, particularly with the confirmation pipeline choked by judicial appointments and pending budget negotiations.
- If the White House delays the nomination until the new Congress convenes in January 2027, any nominee will face rigorous, hostile cross-examination from a Democratic-led Senate eager to investigate the mid-November outage wave, scrutinize the firing of Cairncross, and hold the administration accountable for national infrastructure vulnerabilities.
The situation is further complicated by the ongoing failure to seat a director at CISA. With Michael LoSapio’s nomination effectively abandoned due to his contentious January 6 testimony, the federal government faces the prospect of entering 2027 with both its top strategic post (ONCD) and its top operational defense agency (CISA) operating under temporary, acting leadership.
Congressional committees have already scheduled oversight hearings for early December. Lawmakers intend to haul executives from Microsoft, major airlines, and telecommunications providers before Congress, alongside DHS Secretary Markwayne Mullin and acting director Davies, to establish a complete timeline of the outages and interrogate the administration's defensive failures.
Strategic Roadmap: Restructuring Federal Cyber Resilience
The firing of Sean Cairncross must serve as an inflection point rather than an isolated political headline. If the federal government and private industry treat this episode solely as the personal failure of a single political appointee, the systemic vulnerabilities that precipitated the mid-November collapse will remain unaddressed.
A durable strategy to secure the nation's digital backbone requires three core policy and architectural interventions:
1. Codify Mandatory Canaries and Blast-Radius Limits for Critical Infrastructure Vendors
The federal government can no longer permit enterprise software providers and infrastructure vendors to push simultaneous, automated configuration and patch deployments across sensitive sectors without rigorous verification.
Congress and executive regulators must mandate strict deployment architectures for any commercial provider holding critical infrastructure contracts:
- Canary Deployments: Prohibiting simultaneous global rollouts. Updates must be applied to non-critical, isolated subsets of infrastructure (canaries) and monitored for systemic drift before advancing to broad deployment.
- Air-Gapped Circuit Breakers: Mission-critical operations—such as air traffic routing, classified communications, and financial transaction processing—must maintain decoupled, locally cached operational states capable of surviving complete upstream cloud identity and configuration failures.
- Independent Telemetry Auditing: Mandating that vendors provide federal incident response teams with raw, unmediated telemetry during service disruptions, eliminating the reliance on public status dashboards that obscure the root causes of major systemic failures.
2. Overhaul the Statutory Authority of the ONCD
The ambiguity surrounding the Office of the National Cyber Director must be resolved by statute. Congress must amend the FY2021 NDAA provisions to clearly demarcate where ONCD’s strategic authority ends and CISA’s operational command begins.
If the National Cyber Director is to remain accountable for the nation’s digital posture, the office must be given formal statutory power to:
- Set and enforce mandatory baseline architecture requirements for all civilian federal agencies, overriding individual agency CIO resistance.
- Conduct joint risk reviews with the Office of Management and Budget to freeze procurement funding for agency IT projects that fail basic fault-tolerance standards.
- Exercise formal interagency coordination authority during declared national cyber emergencies, ensuring unified messaging and rapid resource reallocation between civilian and military defensive teams.
3. Move from Monoculture to Distributed Redundancy
The mid-November crisis proved that consolidating federal and commercial operations onto single, proprietary cloud and software ecosystems introduces unacceptable systemic risk.
The administration and enterprise leaders must pivot from theoretical optimization to engineered resilience:
- True Multi-Cloud and Hybrid Redundancy: Federal agencies must be barred from utilizing single-vendor identity architectures. Core public services must maintain hot-standby capabilities across distinct, competing cloud hosting providers to guarantee continuity of operations if an upstream directory provider fails.
- Modernization of Technical Debt: Rather than diverting federal capital into speculative AI initiatives, funding must be directed toward replacing legacy codebases, updating obsolete telecommunications switches, and isolating critical control planes from the broader internet.
What to Watch Next
As Washington navigates the fallout of this personnel shakeup and technical collapse, several critical milestones will indicate whether the federal government is genuinely addressing its digital vulnerabilities:
- The Acting Director's First Moves: Observers must watch whether Kirsten Davies initiates a comprehensive audit of civilian agency cloud dependencies, rolls back Cairncross’s offensive-heavy March strategy, or implements immediate baseline resilience mandates across the federal enterprise.
- The Congressional Inquest: High-stakes hearings scheduled for early December will expose internal communications between the White House, DHS, Microsoft, and the FAA, testing the administration's claim that the outages were entirely accidental rather than an exploited architectural failure.
- The Looming Nomination Showdown: Whether President Trump rushes a permanent nominee for National Cyber Director through the lame-duck Republican Senate or leaves Davies to navigate a hostile Democratic majority in January will signal the administration's long-term strategy for cyber governance.
- The Post-Incident Telemetry Disclosures: Detailed post-mortem reports from the FAA, DHS, and private cloud providers will eventually reveal the exact line-by-line configuration errors that sparked the cascade, providing the broader engineering community with the forensic data necessary to prevent a recurrence.
The mid-November outage wave broke the comfortable illusion that modern technological supremacy protects a nation from systemic collapse. In removing Sean Cairncross, the White House solved an immediate political optics problem. Resolving the underlying technological fragility that triggered the crisis will prove vastly more challenging.
Reference:
- https://www.cbsnews.com/news/white-house-national-cyber-director-sean-cairncross-leaving/
- https://www.thejournal.ie/white-house-fires-cybersecurity-chief-sean-cairncross-after-recent-widespread-outages-7232072-Nov2026/
- https://global.chinadaily.com.cn/a/202611/20/WS6affeb6fe4b03ebf8519db82.html
- https://edition.cnn.com/2026/11/19/politics/national-cyber-director-replaced-sean-cairncross
- https://www.defenseone.com/policy/2026/11/pentagon-cio-replaces-white-house-cyber-director-sean-cairncross-major-shakeup/417359/
- https://www.euronews.com/2026/11/20/white-house-national-cyber-director-fired-after-wave-of-tech-outages
- https://www.theguardian.com/us-news/2026/nov/19/white-house-cyber-director-ousted
- https://gizmodo.com/sean-cairncross-out-as-national-cyber-director-2000842896
- https://en.wikipedia.org/wiki/Sean_Cairncross
- https://www.sicw.gov.sg/speakers/speaker-the-hon-sean-cairncross/