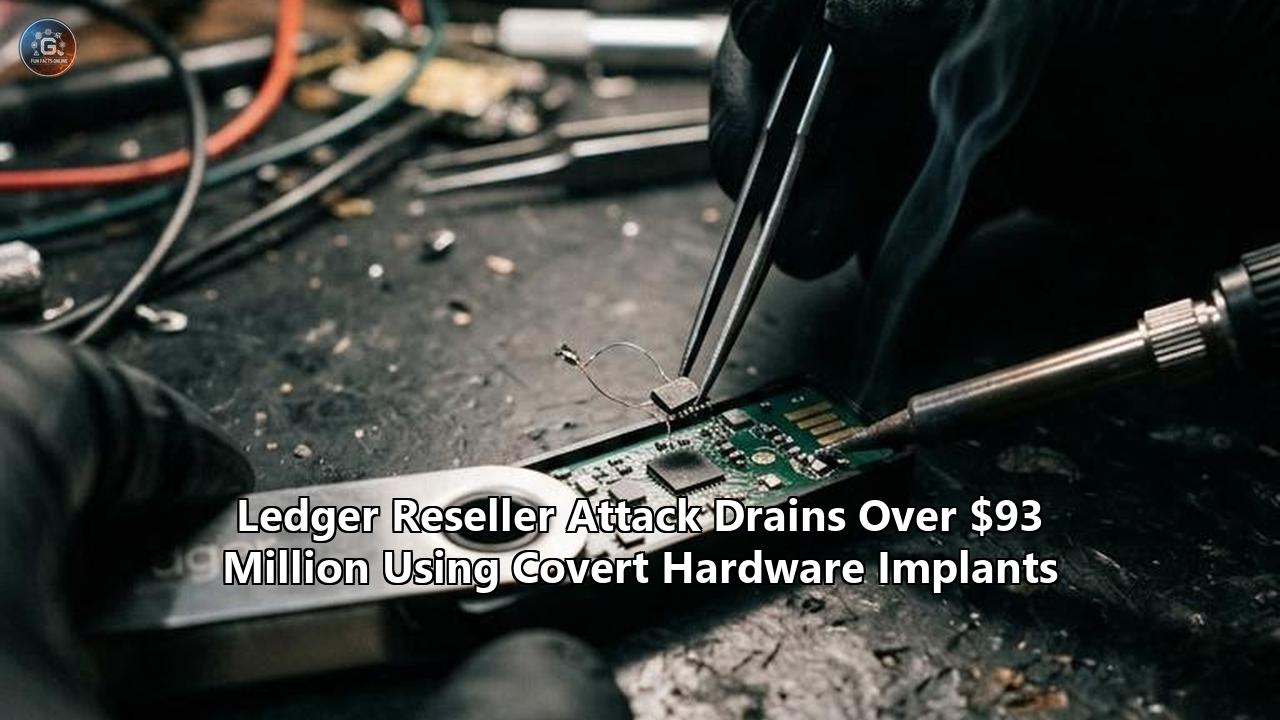
Between October 9 and October 11, 2026, a silent, cross-chain catastrophe swept through the self-custody ecosystem. Without a single compromised private key database, breached cloud server, or deceptive smart contract approval, more than 300 high-value cryptocurrency wallets were systematically cleaned out. Stolen assets—encompassing over 200 Bitcoin, tens of millions of TRC-20 Tether (USDT), and heavy allocations of Ethereum, Solana, and Polygon—surpassed $93 million within forty-eight hours.
The origin of the disaster was not a software vulnerability or a rogue remote firmware update. Instead, security researchers and hardware analysts unraveled an operation long considered theoretical outside nation-state espionage: a physical supply chain interdiction operating through an authorized retail channel.
Ledger, the world’s largest manufacturer of hardware signers, confirmed that units sold through CryptoBilis—an authorized third-party reseller operating across Malaysia, Indonesia, and the wider Southeast Asian market—had been systematically opened, altered, and seeded with covert micro-hardware implants before reaching consumers. Tucked beneath the display screens and wired directly into the display circuitry, micro-controllers paired with embedded eSIMs and LTE antennas captured users’ 24-word recovery phrases the exact moment they were generated, quietly transmitting them to an offshore criminal syndicate.
As law enforcement, blockchain forensics firms, and competing hardware manufacturers sift through the fallout, this Ledger wallet hack represents a watershed moment. It exposed the structural limit of cryptographic chip attestation: a secure element can remain mathematically pure while the physical hardware surrounding it has been completely compromised.
  +-----------------------------------------------------------------+
  |                  FACTORY AUTHENTIC SECURE ELEMENT               |
  |             (STMicroelectronics ST33 - CC EAL6+ Certified)       |
  |                                                                 |
  |  - Cryptographic Root of Trust Intact                           |
  |  - Private Keys Generated via Internal Hardware TRNG             |
  |  - Ledger 'Genuine Check' Attestation: PASSED (Cryptographically)|
  +--------------------------------+--------------------------------+
                                   |
                                   | Raw SPI / I2C Framebuffer Bus
                                   v
  +-----------------------------------------------------------------+
  |               COVERT HARDWARE INTERDICTION POINT                |
  |                                                                 |
  |  +-----------------------------------------------------------+  |
  |  |          Tapped Traces (MOSI / SCLK / Chip Select)        |  |
  |  +-----------------------------+-----------------------------+  |
  |                                |                                |
  |                                v                                |
  |  +-----------------------------------------------------------+  |
  |  |          Covert Secondary Multilayer Flex-PCB             |  |
  |  |                                                           |  |
  |  |  - Ultra-Low-Power Microcontroller (Sniffs Framebuffer)   |  |
  |  |  - Optical Character / Byte Decoder (Parses BIP-39 Words) |  |
  |  |  - Micro-Cellular Modem + Integrated Baseband             |  |
  |  |  - Provisioned Global Roaming eSIM + Planar Antenna       |  |
  |  +-----------------------------+-----------------------------+  |
  +--------------------------------|--------------------------------+
                                   |
                                   | Out-of-Band Exfiltration
                                   | (Encrypted Cell Broadcast)
                                   v
  +-----------------------------------------------------------------+
  |            ADVERSARY COMMAND-AND-CONTROL (C2) SERVERS           |
  |                                                                 |
  |  - Harvests 24-Word Seed Phrases Out-of-Band                    |
  |  - Silent Staging: Multi-Week Sleep Cycles                      |
  |  - Coordinated Mass-Drain Sweep (Bypasses Ledger Live Entirely) |
  +-----------------------------------------------------------------+
                                   |
                                   | Visual Display to User
                                   v
  +-----------------------------------------------------------------+
  |                    OLED / E-INK DISPLAY PANEL                   |
  |                                                                 |
  |  "Write down Word #1: abandon ... Word #24: zoom"              |
  |                                                                 |
  |  Targeted User faithfully records words on paper recovery sheet |
  |  assuming isolation from the internet.                          |
  +-----------------------------------------------------------------+
Anatomy of the Hardware Tap: How the LTE Implant Works
To understand why this attack went undetected across hundreds of initial setups, one must look directly at the internal silicon architecture of modern hardware signers. A device like the Ledger Nano X relies on a split-architecture design. Sensitive cryptographic operations—seed generation via an internal True Random Number Generator (TRNG), private key derivation, and transaction signing—occur entirely inside a Secure Element (typically an STMicroelectronics ST33-series microchip certified to Common Criteria EAL6+). A secondary general-purpose microcontroller (such as an STM32) handles non-critical peripheral operations: processing USB communication, maintaining Bluetooth Low Energy (BLE) connectivity, handling physical button presses, and driving the display panel.
The architectural vulnerability exploited here did not lie in the Secure Element. Instead, it targeted the "analog hole" of hardware security: the unavoidable reality that human users must visually verify their cryptographic seed phrase.
+------------------------------------------------------------------------------------+
|                             DEVICE INTERNAL ARCHITECTURE                           |
|                                                                                    |
|   +-----------------------+              Raw Bus               +---------------+   |
|   |    Secure Element     |-----------------+----------------->|  OLED Screen  |   |
|   | (ST33 Cryptographic)  |                 |                  | (Visual Mnemonic) |
|   +-----------------------+                 |                  +---------------+   |
|                                             |                                      |
|                                             v Physical Tap                         |
|                            +---------------------------------+                     |
|                            |         COVERT IMPLANT          |                     |
|                            |  - Framebuffer Parser MCU       |                     |
|                            |  - Cellular Baseband + eSIM     |                     |
|                            |  - Planar RF Micro-Antenna      |                     |
|                            +----------------+----------------+                     |
|                                             |                                      |
+---------------------------------------------|--------------------------------------+
                                              | 4G LTE-M / NB-IoT
                                              v
                              +--------------------------------+
                              |   Attacker Collector Servers   |
                              +--------------------------------+
Teardowns conducted by independent security researchers, corroborated by former Mt. Gox chief executive Mark Karpelès via Tibane Labs and subsequently verified by Ledger’s internal Donjon research team, revealed an astonishingly compact engineering footprint.
Attackers designed a custom, multi-layer flexible printed circuit board (flex-PCB) that was physically spliced into the internal wiring harness. In several examined Nano X devices, the module was tucked into the tight physical void behind the display screen—occupying the space normally reserved for shock-absorbing display foam. In another examined variant, attackers went so far as to unseat the stock rechargeable lithium-ion battery, substituting a custom cell with a slightly reduced milliamp-hour capacity to free up approximately 1.8 millimeters of clearance inside the casing.
The malicious board integrated three primary components:
- An ultra-low-power micro-controller (MCU) designed to passively snoop the serial peripheral interface (SPI) or display bus running between the device's processor and the screen.
- A surface-mount cellular modem supporting low-power LTE-M and NB-IoT protocols.
- An integrated eSIM module provisioned with global roaming profiles, wired to a micro-strip patch antenna adhered to the inside edge of the plastic chassis.
During the initial device configuration, the Secure Element executes its BIP-39 initialization protocol. Because hardware wallets are deliberately kept air-gapped from computers during seed creation, the device instructs the user to write down 24 English words shown sequentially on the display screen.
As the display driver clocked raw character byte streams across the internal bus, the implant's microcontroller scraped the serial data. The attackers had pre-programmed the chip's lightweight firmware with a regex-style parser calibrated to recognize the BIP-39 standardized dictionary of 2,048 words. As the user toggled through words 1 through 24 using the hardware’s physical buttons, the implant silently buffered the strings.
Once the 24th word was verified, the implant's logic asserted a wake signal on the cellular baseband. Operating on low-power radio bands that draw minimal power from the device's main power rail, the modem executed a rapid, lightweight handshake with local cellular towers. Within milliseconds, it transmitted a compact, encrypted UDP payload containing the extracted mnemonic seed, the device's hardware identifier, and a timestamp to an offshore command-and-control (C2) server.
Because the exfiltration relied on independent cellular data, it left zero trace on the user's host computer or local Wi-Fi network. A network engineer monitoring host USB traffic through tools like Wireshark would have seen nothing more than standard Human Interface Device (HID) packets traveling between the Ledger device and the Ledger Live client application. To the operating system and the local network, the device was completely offline. In reality, it was transmitting over the mobile network.
The Cryptographic Blind Spot: Why Genuine Check Passed
The revelation that modified signers were circulating in the wild ignited widespread outrage among users who believed they had verified their devices cryptographically. For nearly a decade, Ledger’s primary defense against supply chain tampering has rested on its proprietary "Genuine Check" mechanism. Every official setup sequence requires the user to plug the wallet into Ledger Live, which conducts a challenge-response verification designed to authenticate the machine’s internal provenance.
+---------------------------------------------------------------------------------------+
|                         THE GENUINE CHECK CHALLENGE-RESPONSE                          |
|                                                                                       |
|   +---------------+         1. Sends Ephemeral Nonce R        +-------------------+   |
|   |  Ledger Live  |------------------------------------------>|  Secure Element   |   |
|   |  Root Server  |                                           |  (ST33 Chip)      |   |
|   +---------------+         2. Signs R with Root Private Key  +-------------------+   |
|           |       <-------------------------------------------          |             |
|           v                                                             v             |
|   Cryptographic Proof                                           Untouched Silicon     |
|   Validates: PASSED                                             Ignores Display Tap   |
+---------------------------------------------------------------------------------------+
Every single device compromised in this incident sailed through the Genuine Check without raising a single red flag.
The technical reality behind this failure exposes the inherent boundaries of public-key attestation. During factory production at Ledger’s facility in Vierzon, France, each Secure Element is provisioned with a unique asymmetric private key paired to a factory certificate signed by Ledger’s private Certificate Authority (CA). When Ledger Live initiates the Genuine Check:
- Ledger's attestation server generates a cryptographic challenge (a random number, or nonce).
- The nonce is passed over the USB bus into the Secure Element.
- The Secure Element calculates a digital signature over that challenge using its internally burned private key and returns the signature to Ledger's verification servers.
- The server verifies the signature against its public certificate database. If the mathematical proof aligns, Ledger Live declares the hardware authentic.
In this Ledger wallet hack, the attackers never tampered with the Secure Element. They did not extract its private attestation key, nor did they alter the device’s custom operating system, BOLOS (Blockchain Open Ledger Operating System).
Because the Secure Element was completely original, every cryptographic challenge received by the device was processed by authentic hardware. The Secure Element signed the challenge correctly, Ledger Live validated the signature, and the client application displayed its reassuring green checkmark: "Your Ledger is genuine."
Ledger’s internal threat model had long conceded that its Genuine Check was blind to peripheral man-in-the-middle implants that leave the central cryptographic processor intact. The company historically argued that installing an implant complex enough to sniff signals and exfiltrate data without triggering internal power anomalies or breaking the outer enclosure was economically and technically unfeasible for broad criminal deployment. The $93 million heist shattered that security assumption.
Supply Chain Interdiction: The Weaponization of CryptoBilis
A hardware attack of this complexity cannot occur on a manufacturing assembly line without immediate detection from quality-control automated test equipment (ATE). The attackers chose a point in the logistics journey where hardware signers are most vulnerable: the regional authorized reseller.
+------------------------------------------------------------------------------------+
|                         SUPPLY CHAIN INTERDICTION PIPELINE                         |
|                                                                                    |
|  [Ledger Factory (France)]                                                         |
|             |                                                                      |
|             v (Legitimate Freight)                                                 |
|  [Authorized Reseller: CryptoBilis (Southeast Asia)]                               |
|             |                                                                      |
|             v (Corporate Interception / Ownership Shift)                           |
|  [Interdiction Facility / Lab]                                                     |
|     * Precision Box De-Sealing                                                     |
|     * Chassis Split & Display Wire Harness Splicing                                |
|     * Flex-PCB Cellular Implant Soldered Behind Screen                             |
|     * Factory-Grade Plastic Re-Shrink-Wrapping                                     |
|             |                                                                      |
|             v (Restocked Into Distribution Warehouse)                              |
|  [Unsuspecting End Consumers & Sub-Retailers]                                      |
+------------------------------------------------------------------------------------+
The focal point of the compromise was CryptoBilis, a long-standing, officially certified Ledger partner serving Malaysia, the Philippines, and Singapore. For years, security-conscious cryptocurrency holders across the region had purchased devices from CryptoBilis precisely to avoid the risks of buying hardware signers from unvetted third-party marketplaces such as eBay, Amazon, or Shopee.
Corporate registries and supply-chain intelligence reviewed by investigators indicate that CryptoBilis had undergone an unannounced structural shift earlier in 2026. Former operational executives of the company revealed that equity control had been transferred to an opaque investment entity registered in Hong Kong. Following the transaction, employees were bound by aggressive non-disclosure agreements.
Shortly after this ownership pivot, the interdiction began. Genuine Ledger Nano X and Ledger Flex devices delivered to the reseller's regional warehouses were diverted to a secondary engineering facility before distribution.
Investigators found that the modifications were performed with remarkable mechanical precision. The tamper-evident shrink wrap on the packaging was carefully matched or duplicated using industrial heat guns and retail-grade polyolefin film. The plastic sonic welds and internal chassis clips of the signers were split along factory seams using micro-blade tools, leaving zero external marring.
The flex-PCBs used for the implants were not hand-soldered prototype boards; they were industrially manufactured, surface-mounted circuit boards made in commercial fabrication houses. The solder joints bridging the display traces to the implant were laid down with microscopic precision using hot-air rework stations, and the devices were sealed back into their retail packaging with complete sets of unblemished accessories, warranty cards, and paper recovery sheets.
+--------------------------------------------------------------------------------+
|                         HARDWARE ATTACK VECTORS COMPARED                       |
+--------------------+-----------------------+------------------+----------------+
| Vector             | Technical Target      | Attestation Status| Exfiltration   |
+--------------------+-----------------------+------------------+----------------+
| Evil Maid Attack   | Microcontroller / USB | Fails Check      | Host USB / PC  |
| Malicious Firmware | Operating System / MCU| Fails Attestation| Host Software  |
| Covert Display Tap | Screen SPI / I2C Bus  | Passes Genuine   | Cellular LTE-M |
|                    |                       | Check            | (Out-of-band)  |
+--------------------+-----------------------+------------------+----------------+
The altered inventory was moved back into CryptoBilis’s fulfillment queues and pushed out across multiple consumer touchpoints. In addition to direct online orders, modified stock found its way into commercial retail outlets, including electronic storefronts at Singapore’s Changi Airport (operating under the Metapod brand) and primary tech corridors in Kuala Lumpur and Manila.
The scale of this Ledger wallet hack exposed a long-denied systemic blind spot: a user can follow every orthodox rule of self-custody—buying from an authorized distributor, checking physical seals, passing hardware attestation, and running setups on air-gapped tables—and still be compromised before their fingers ever touch the buttons.
From Hand-Soldered Prototypes to Mass Production: The Hardware Evolution
Evidence gathered across forensic tear-downs demonstrates that the attackers did not deploy their operation overnight. Analysis from Tibane Labs revealed three distinct generations of hardware implants, highlighting an extensive period of iteration and operational refining.
+-------------------------------------------------------------------------------+
|                            IMPLANT DESIGN EVOLUTION                           |
|                                                                               |
|  [Generation 1: Lab Prototype]                                                |
|    - Discrete micro-wires manually soldered to display pins                   |
|    - Bulky standard microcontroller                                           |
|    - External trace modifications visible under basic disassembly             |
|                                                                               |
|  [Generation 2: Hybrid Custom Board]                                          |
|    - Custom two-layer flex-PCB tucked beneath battery enclosure               |
|    - Battery cell modified: capacity shaved down to clear 1.8mm z-height      |
|    - First integration of eSIM cellular micro-modem                           |
|                                                                               |
|  [Generation 3: Industrial Production Module]                                 |
|    - Multi-layer flex-PCB replacing factory display cushion entirely          |
|    - Zero battery modification required on larger form factors (Ledger Flex)  |
|    - Low-frequency planar antenna integrated directly onto the PCB edge       |
|    - Automated character buffer parsing BIP-39 mnemonic byte streams         |
+-------------------------------------------------------------------------------+- Generation 1 (Early 2026): The earliest iterations discovered in non-drained test units recovered from grey-market sources featured hand-soldered enamel-coated micro-wires linking the display pins of the microcontroller directly to a small daughterboard. These prototypes were mechanically fragile and occasionally caused display flickering, a telltale sign that could alert an observant user.
- Generation 2 (Summer 2026): Attackers transitioned to custom two-layer flex-PCBs that integrated the display connector directly. The daughterboard was reduced to less than 0.8 millimeters in thickness, utilizing a high-density interconnector (HDI) layout. The micro-controller was upgraded to run an energy-harvesting loop, waking only when power surged through the display traces during screen updates.
- Generation 3 (Deployed Autumn 2026): The hardware reached its industrial peak. As documented during teardowns of affected units bought at Singapore Changi Airport and through regional distribution, the implant had been upgraded to a multi-layer board with an onboard planar inverted-F antenna (PIFA). In newly released hardware form factors such as the Ledger Flex, the larger internal volume allowed the attackers to integrate the implant without modifying the battery at all, placing the espionage layer seamlessly inside the display bracket.
The operational sophistication matched the hardware execution. Forensic researchers discovered that the criminal group did not begin sweeping wallets as soon as recovery phrases were captured. Instead, they observed absolute silence for months.
Data compiled by blockchain analytics firm Bitquery confirmed that more than 80% of the addresses emptied on October 9 had received their initial deposits as early as June 2026. The attackers spent months stockpiling recovery phrases on encrypted collector servers, waiting until their retail campaign had seeded a massive pool of capital before launching a synchronized exfiltration strike.
The Coordinated Heist: Timing, On-Chain Flow, and Laundering
At 02:14 UTC on October 9, the strike was triggered. Using automated liquidation bots interacting directly with blockchain RPC nodes, the attackers bypassed front-end interfaces like Ledger Live entirely. The attackers derived the master private keys from the harvested BIP-39 seed phrases, loaded the keys into programmatic signing scripts, and executed parallel drains across hundreds of addresses simultaneously.
+------------------------------------------------------------------------------------+
|                         CROSS-CHAIN LIQUIDATION ARCHITECTURE                       |
|                                                                                    |
|                  Harvested BIP-39 Master Recovery Phrases                          |
|                                     |                                              |
|                                     v                                              |
|            Parallel Signing Scripts on Adversary RPC Node Cluster                  |
|                                     |                                              |
|        +----------------------------+-----------------------------+                |
|        |                            |                             |                |
|        v                            v                             v                |
|  [Tron Network]             [Bitcoin Network]            [Ethereum & EVM Chains]   |
|   - $70.4M USDT Swept        - 211 BTC ($17.5M) Swept     - ~$5.3M Native & ERC-20 |
|        |                            |                             |                |
|        +--------------+             |                             |                |
|                       |             v                             v                |
|                       |      UTXO Peeling Chains          Tornado Cash Pools       |
|                       |      & CoinJoin Routes            & Uniswap Liquidity      |
|                       v                                                            |
|          Centralized Asset Intervention                                            |
|          * Tether Freezes $10M USDT on Tron                                        |
|          * ~$60M USDT Routed to Instant DEX Swaps                                  |
+------------------------------------------------------------------------------------+
The scale of the sweep was brutal in its speed and breadth:
- TRON (TRC-20 USDT): Over $70 million in Tether was siphoned from more than 180 addresses within twenty minutes. The attacker immediately pushed these funds through high-volume liquidity pools on SunSwap and decentralized cross-chain bridges, swapping stablecoins into Tron (TRX) and bridging into Bitcoin and Ethereum.
- Bitcoin (BTC): More than 211 BTC—valued at over $17.5 million—was swept from legacy, SegWit, and Native SegWit addresses. The funds were moved through rapid UTXO-peeling chains before being routed through Wasabi-style coin-join transactions and cross-chain atomic swaps into privacy-centric assets like Zcash (ZEC).
- Ethereum & EVM Chains (BNB Chain, Polygon): Over $5 million in native Ether, wrapped tokens, and stablecoins was drained. Attacking wallets systematically swept tokens using automated approvals, routed them through decentralized aggregator smart contracts, and deposited the converted ETH directly into Tornado Cash in batches of 10 and 100 ETH.
- Solana (SOL): More than $2 million in SOL and SPL tokens was converted via Raydium and bridged off-chain.
The speed of the operation initially triggered confusion within cybersecurity circles, with early commentary hypothesizing that an adversary had extracted Ledger’s master firmware signing keys or discovered an algorithmic weakness in the Secure Element's pseudo-random number generation.
As blockchain investigator Specter and on-chain intelligence teams traced the transaction flows, a curious pattern emerged: victims were concentrated in Southeast Asia, with secondary victims popping up in Germany and Singapore. The one unifying thread tying together a crypto whale who lost 80 BTC ($4.8 million) in a single transaction and a retail user who lost $1,500 in USDT was not their network setup, operating system, or device firmware version—it was where the hardware signer was purchased.
Tether acted with unusual speed, freezing approximately $10 million in USDT across multiple recipient addresses on the Tron blockchain after being alerted by exchange partners. However, the overwhelming majority of the capital—more than $80 million—escaped into the decentralized mixing infrastructure before centralized stablecoin issuers or law enforcement could intervene.
Supply Chain Realities: The Global Distributor Blind Spot
The crisis at CryptoBilis ignited a severe reassessment of authorized reseller networks across the cryptocurrency ecosystem. Hardware manufacturers have historically relied on third-party regional distributors to minimize shipping overhead, clear national customs barriers, and satisfy local consumer protection statutes.
Within days of the attack’s disclosure, the structural vulnerabilities inherent to this model became undeniable. Reports surfaced in Europe that altered Ledger units had appeared on retail shelves outside Southeast Asia. A European user identified as Johannes published teardowns of two separate Ledger Nano X devices purchased at branch locations of MediaMarkt—Europe's largest consumer electronics retailer. Photographs confirmed that the units contained secondary flex-PCBs soldered across the display traces, bearing design markers identical to the early-generation implants identified in Malaysia.
MediaMarktSaturn Retail Group moved immediately, issuing a total stop-sale order and stripping every Ledger device from the shelves and web listings of its more than 1,000 stores across Europe. Ledger followed by ordering distributors across seven Asian markets to freeze sales and return unsplit inventory for laboratory validation.
The competitive fallout was immediate. Open-source rival Trezor announced it would dissolve 95% of its global third-party reseller contracts by January 2027, moving to a direct-to-consumer logistics model where all shipments originate from factory hubs equipped with physical tamper seals and tamper-evident packaging. OneKey, another prominent hardware manufacturer, halted all reseller inventory dispatches while initiating a top-to-bottom audit of its supply chain.
+------------------------------------------------------------------------------------+
|                         RESELLER MODEL CRISIS & RESPONSES                          |
|                                                                                    |
|  [Hardware Manufacturer]                                                           |
|             |                                                                      |
|             v                                                                      |
|  [Global Reseller Network] <--- ATTACK SURFACE (Weakest Link)                      |
|             |                                                                      |
|             +---------> [Trezor Response]                                          |
|             |             - Cuts 95% of third-party resellers                      |
|             |             - Retains only direct, factory-to-consumer fulfillment   |
|             |                                                                      |
|             +---------> [OneKey Response]                                          |
|             |             - Immediate shipment freeze across distributors          |
|             |             - Forensic hardware audits of existing stock             |
|             |                                                                      |
|             +---------> [Retail Chains (e.g., MediaMarkt)]                         |
|                           - Global stop-sale orders across 1,000+ retail hubs      |
|                           - Full inventory recalls for laboratory screening        |
+------------------------------------------------------------------------------------+
Yet, supply chain experts emphasize that eliminating resellers does not eliminate supply chain interdiction; it merely shifts the interdiction target further back toward freight forwarders, customs checkpoints, and postal handlers.
Unlike typical phishing schemes or web3 credential harvesting, this Ledger wallet hack bypassed every digital checkpoint because the attack manipulated the physical space between the digital sign-off and the human eye. If an adversary controls the physical device prior to unboxing, conventional cryptographic guarantees break down.
Architectural Lessons: Beyond the Analog Hole
The $93 million CryptoBilis breach has permanently altered the engineering parameters of secure hardware manufacturing. The realization that factory-grade attestation mechanisms such as Ledger's Genuine Check can validate a device housing a malicious cellular transmitter has forced an industry-wide reassessment of how hardware signers must be constructed.
Moving forward, hardware designers are converging on several architectural solutions to close the analog gap:
1. Encrypted Display Interfaces
The primary vulnerability exploited by the covert implant was the cleartext nature of the display bus. Because raw pixel commands and ASCII byte streams traveled unencrypted from the processor to the screen, any passive bus sniffer could parse the mnemonic phrase.
Future hardware generations must implement display-level cryptographic encapsulation, running point-to-point authenticated encryption (such as authenticated AES-GCM or MIPI DSI with frame-level encryption) between the Secure Element silicon and an integrated display controller buried beneath the glass panel. If the signals running across the board are encrypted, a passive flex-PCB tap captures nothing but unintelligible ciphertext.
+-------------------------------------------------------------------------------+
|                           PROPOSED DEFENSIVE ARCHITECTURE                     |
|                                                                               |
|  +---------------------+                               +------------------+   |
|  |   Secure Element    |                               |  Display Panel   |   |
|  |  (Cryptographic OS) |                               |  Glass Substrate |   |
|  +----------+----------+                               +--------+---------+   |
|             |                                                   ^             |
|             | Point-to-Point Encrypted Bus                      |             |
|             | (AES-GCM Authenticated Stream)                    |             |
|             +===================================================+             |
|                                                                               |
|      * Any passive flex-PCB tap captures only random ciphertext               |
|      * Active enclosure mesh triggers capacitive tamper erase                 |
|      * Transparent optical casing allows immediate visual inspection          |
+-------------------------------------------------------------------------------+
2. Active Enclosure Monitoring & Potting
Consumer hardware signers have favored sleek, clip-together plastic enclosures that can be separated and resealed without visual damage.
Industrial security designs, such as high-security Point of Sale (POS) terminals, encase their primary processing components in solid structural resin (potting) or wrap the internal chassis in an active capacitive tamper mesh. If a tool breaches the casing or an added circuit board changes internal capacitance, the secure element automatically purges its non-volatile memory and wipes its attestation keys.
3. Transparent Enclosures and Visual Inspection
The crypto hardware space is seeing renewed interest in transparent polycarbonate casings, long championed by open-hardware advocates. While a clear casing does not stop microscopic modifications, it makes installing a secondary flex-PCB, cellular antenna, or replacement battery immediately apparent to the buyer.
4. Transition to Multi-Party Computation (MPC) and Multisig
For institutions and high-net-worth individual investors, the reverberations of this Ledger wallet hack have accelerated a decisive move away from single-signature consumer hardware dongles.
A user relying on a 2-of-3 multisignature architecture across diverse hardware vendors (e.g., combining a Ledger, a Trezor, and a Coldcard) remains completely protected against a supply chain breach of any single manufacturer. Even if an implant in one device captures a recovery phrase, that stolen seed alone is insufficient to move funds without signatures from the remaining independent devices.
The Immediate Action Checklist for Hardware Wallet Users
With secondary distribution channels worldwide under active investigation, anyone holding cryptocurrency secured by a hardware wallet must treat supply chain verification as an urgent security priority.
+------------------------------------------------------------------------------------+
|                         REMEDIATION & RECOVERY PROTOCOL                            |
|                                                                                    |
|  Step 1: Audit Device Origin                                                       |
|    - Purchased from CryptoBilis, airport kiosks, or unverified distributors?       |
|                                                                                    |
|  Step 2: Assess Device Status                                                      |
|    +--------------------------------+--------------------------------+             |
|    | ALREADY INITIALIZED?           | UNOPENED / UNINITIALIZED?      |             |
|    +--------------------------------+--------------------------------+             |
|    | - DO NOT enter seed elsewhere. | - DO NOT power on or setup.    |             |
|    | - Deploy fresh clean signer.   | - Quarantine unit immediately. |             |
|    | - Migrate funds to clean seed. | - Contact vendor forensics.    |             |
|    +--------------------------------+--------------------------------+             |
|                                                                                    |
|  Step 3: Establish Multisig / Institutional Custody                                 |
|    - Remove single-point-of-failure hardware dependencies.                         |
+------------------------------------------------------------------------------------+
Security teams and forensic researchers advise the following steps:
- Verify Sourcing History: Check procurement records for all hardware signers. Any device acquired through CryptoBilis, retail kiosks at international airports (including Metapod at Changi), or secondary electronics outlets such as MediaMarkt over the past 12 months should be treated as compromised.
- Never Re-Enter an Exposed Seed: If an existing hardware wallet was configured on an altered device, simply transferring the mnemonic phrase to a new, secure device fixes nothing. The original 24 words were captured the second they were generated and are stored on adversary infrastructure. Users must generate a clean seed phrase on a verified, secure device and execute an on-chain migration of all assets.
- Quarantine Uninitialized Units: If you hold an uninitialized device purchased from an affected reseller, do not power it on. Powering up the hardware allows the implant to run its initialization sequence. Contact the manufacturer's forensic division to coordinate an exchange and physical examination.
- Implement Multisig Configurations: Eliminate the reliance on any single consumer hardware vendor. Transition vault storage to multi-institution MPC setups or n-of-m multisig protocols utilizing hardware from disparate manufacturers with contrasting supply chains.
As investigations widen across international jurisdictions, the CryptoBilis incident stands as an enduring case study in modern threat models. When digital security is mathematically sound, the adversary inevitably pivots to the physical world—proving that the hardest link to protect in cryptography is the real-world hardware held in human hands.
Reference:
- https://www.tradingview.com/news/cryptobriefing:f44864c40094b:0-hackers-reportedly-drain-up-to-93-million-through-compromised-ledger-reseller/
- https://chainup.com/blog/ledger-cryptobilis-attack-hardware-wallet-limits-mpc-custody/
- https://bitcoinmagazine.com/news/ledger-says-crime-group-spent-millions
- https://cryptobriefing.com/ledger-cryptobilis-hardware-implant-draining/
- https://cryptobriefing.com/ledger-supply-chain-attack-crypto-scammer-btc/
- https://www.tomshardware.com/tech-industry/cryptocurrency/ledger-to-review-sales-and-anti-tamper-policies-after-usd93-million-hardware-wallet-supply-chain-attack-rogue-lte-implants-reportedly-stole-users-recovery-phrases
- https://www.binance.com/en/square/post/376791560599059
- https://www.helpnetsecurity.com/2026/10/12/ledger-wallets-compromised-via-hardware-implant/
- https://gizmodo.com/ledger-confirms-how-spy-implants-steal-crypto-from-its-devices-as-cases-spread-2000825324
- https://ambcrypto.com/trezor-supply-chain-security-is-never-finished-tightens-reseller-checks-after-ledger-supply-chain-scare/
- https://thedefiant.io/news/security/ledger-says-cryptobilis-sold-wallet-implants-transmit-recovery-phrases-over-lte
- https://qz.com/ledger-reseller-controls-spy-chip-crypto-theft-101426
- https://www.halborn.com/blog/post/explained-ledger-supply-chain-attack-october-2026
- https://www.kucoin.com/news/flash/ledger-flex-devices-found-with-spy-modules-over-86m-stolen-previously
- https://www.helpnetsecurity.com/2026/10/12/ledger-wallets-compromised-via-hardware-implant/
- https://cryptoslate.com/ledger-confirms-hidden-implant-in-crypto-wallet-as-93-million-theft-investigation-widens/
- https://changenow.io/blog/ledger-cryptobilis-hack
- https://thedefiant.io/news/security/ledger-user-reports-hardware-implant-in-wallet-bought-in-europe
- https://primexbt.com/news/ledger-wallets-sold-by-southeast-asian-reseller-allegedly-carried-implants-in-th/
- https://cryptobriefing.com/criminals-steal-90m-tampered-hardware-wallets/